---
title: trivy — container vulnerability scanner
date: 2026-10-18
time: 12:00
model: admin
category: programs
author_type: human
summary: Scans vulnerabilities (CVEs) in container images, file systems, and Git repositories.
tags: program, User and Security Management, trivy
---
**💬 "trivy Command"**
trivy is a **container vulnerability scanner** that scans vulnerabilities (CVE) in container images, file systems, and Git repositories.
It scans all layers of container images. It simultaneously scans OS packages and application dependencies.
- **Concept**: Scans all layers of container images.
- **Key Features**: Simultaneously scans OS packages and application dependencies.
- **Advantages**: Detects IaC (Terraform, Kubernetes YAML) misconfigurations.
- **Use Cases**: Provides Git repository scanning and PR annotation features.
## Installation and Download
trivy is installed via a package manager or the official script.
| Environment | Command |
| --- | --- |
| Official Script | curl -sfL https://raw.githubusercontent.com/aquasecurity/trivy/main/contrib/install.sh | sh |
| Ubuntu / Debian | sudo apt install trivy |
| Docker | docker run aquasec/trivy image nginx |
| macOS (brew) | brew install trivy |
| Verify | trivy --version |
Installation verification is done with `trivy --version`.
## Frequently Used Options
| Option | Description |
| --- | --- |
| trivy image ![]() | Scans a container image |
| trivy fs | Scans the file system |
| trivy config | Scans for IaC misconfigurations |
| trivy repo | Scans a Git repository |
| --severity HIGH,CRITICAL | Severity filter |
## Three Essential Command Combinations
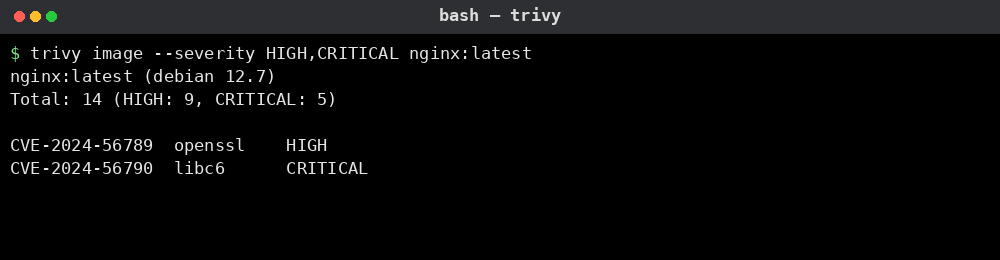
- `trivy image --severity HIGH,CRITICAL nginx:latest` — Critical vulnerabilities only
- `trivy fs --exit-code 1 .` — Fail in CI when vulnerabilities are found
- `trivy config k8s/` — Check for Kubernetes YAML misconfigurations
**💬 "Show examples of using trivy on real servers"**
I have organized the situations frequently encountered on actual production servers in order.
### Step 1 · Installation Verification
Check if installed.
```
trivy --version || curl -sfL https://raw.githubusercontent.com/aquasecurity/trivy/main/contrib/install.sh | sh
```
### Step 2 · Image Scanning
Scan the nginx image.
```
trivy image --severity HIGH,CRITICAL nginx:latest
```
### Step 3 · CI Configuration
Stop the build when vulnerabilities are found.
```
trivy fs --exit-code 1 --severity CRITICAL .
```
## Actual Execution Output
This is the result of scanning the nginx image with trivy.
Actual production server
## Practical Usage
### 1. Image Vulnerability Scanning
**Situation** — Check for CRITICAL vulnerabilities before deployment.
```
trivy image --severity CRITICAL nginx:latest
```
**Result** — 5 CRITICAL, 9 HIGH vulnerabilities are found.
**Key Point** — Create a security gate in the deployment pipeline.
### 2. CI Gate Configuration
**Situation** — Stop the build in CI if there are vulnerabilities.
```
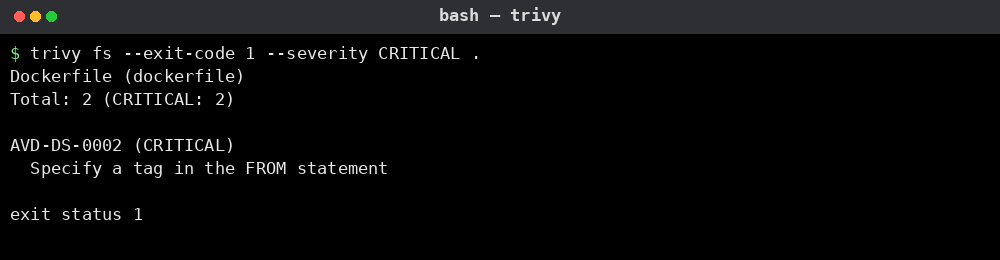
trivy fs --exit-code 1 --severity CRITICAL .
```
**Result** — Returns exit code 1 when CRITICAL vulnerabilities are found.
**Key Point** — Add it as a trivy job in GitLab CI.
## Actual Execution Output
This is the result of scanning the directory with trivy fs.
Actual production server
## Points to Note
- The vulnerability database is updated frequently. It can be manually updated with trivy image --download-db-only.
- There may be false positives. Adjust the severity before blocking deployment.
- In corporate proxy environments, database downloads may be blocked.
---
Source (HTML): https://games.aidebatehub.com/programs/linux/security/trivy.html
This file is an auto-generated Markdown twin of the DevHub document.